Related Posts Plugin for WordPress, Blogger...
Powered by Blogger.
Free Content
Custom Search
Showing posts with label technology. Show all posts

 
 The store looks every bit like Apple Stores found all over the world. PHOTO: REUTERS
SHANGHAI: Chinese counterfeiters have had a field-day pumping out knockoffs of Apple Inc’s best-selling iPhones and iPads but one appears to have gone a step further – a near flawless fake Apple Store that even employees believe is the real deal.

The store in Kunming was stumbled upon by a 27-year-old American blogger living in the city, the capital of China’s mountainous southwestern Yunnan province.

Complete with the white Apple logo, wooden tables and cheery staff claiming they work for the iPhone maker, the store looks every bit like Apple Stores found all over the world, according to the blogger, who goes by the name “BirdAbroad.”

But Apple has no stores in Kunming and only 13 authorized resellers in the city, who are not allowed to call themselves Apple Stores or claim to work for Apple.

“This was a total Apple store rip-off. A beautiful rip-off – a brilliant one – the best rip-off store we had ever seen,” the anonymous blogger posted Wednesday. “Being the curious types that we are, we struck up some conversation with these salespeople who, hand to God, all genuinely think they work for Apple.”

It was unclear whether the store was selling fake or genuine Apple products – there are countless unauthorized resellers of Apple and other brands’ electronic products throughout the country who sell the real thing but obtain their goods by buying them overseas and smuggling them into the country to skip tax.

The store had sections devoted to different Apple products, similar to real Apple stores, and large posters advertising the iPhone 4 and MacBook Pro, according to photos on the blog. (http://birdabroad.wordpress.com/2011/07/20/are-you-listening-st

eve-jobs/)

Apple declined to comment. The Cupertino, California-based firm reported forecast-smashing results Tuesday, helped by massive growth in Asia, and China in particular.

Shady Origins

Apple, which was slow to establish its brand in China, currently has four retail outlets in Beijing and Shanghai. The firm plans another two more this year, including one in Shanghai and another in Hong Kong.

But the immense popularity of Apple’s iPads, iPhones and Macbook computers has spurred a bumper crop of resellers with dubious credentials.

At one unauthorized Apple reseller in Shanghai visited on Thursday, the shop was decorated in much the same way as Apple stores, with wooden tables and chairs with iPads laid out for customers to try out.

The shop was not contained on a list of authorized Apple resellers in Shanghai.

But the proprietors fell short on the attention to detail displayed by their counterparts in Kunming. For one, the store also sold some other products, like chocolate jigsaw puzzles, that would never see the light of day at a real Apple Store.

“Do you have a web camera for my Macbook?,” asked one customer.

“No, but our other store in Lujiazui should have it,” said the sales representative, referring to Apple’s genuine retail store in the heart of Shanghai’s financial district.

When approached, none of the staff claimed to work for Apple or that the store was an actual Apple Store. Customers appeared unfazed.

“I prefer to get my Apple products fixed here. It’s very troublesome going to the real Apple store in Lujiazui because not only do you have to pay to get repairs, but you have to make an appointment to see the sales specialist,” said Xavier, a 30-something expatriate who declined to give his last name.

“The prices are the same as the real store but the service is better here,” he added, before whipping out his two iPads to tinker with.

One of the most frustrating things in life is a slow computer.
Every few years, we buy an expensive new PC and love how fast it starts up, runs programs, and loads websites.  Inevitably though, it starts to slow down until eventually we are pulling our hair out waiting for it to do routine tasks.
https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEjSOYPgbC3Q-IQ5_Aga__HNV7GEQqd96qdeDz2bdQjMIivnJa96NRT7lNw69x5Qfrcbvy2FGZW-2Au6pqiOgR_DeNcCy5JVE9j5vZ4jndlW0lSnWGyvbslmXErNb69chnBt5LN_57rJR-0/
Why is this?  It turns out the answer is actually quite simple and you don't even need to be "technical" to understand the causes and solutions.

The good news: It's not the computer hardware that's the problem.  In most cases, the hardware you have is perfectly capable of being restored to its original glory and kept in fast running condition with minimal effort.

Rather, the problem lies with changes that occur to the PC's software.  The two most common causes of slowdown (along with easy solutions) are:

1. The most common problem: registery errors

Every time you (or your kids) load a program, game, or file, your PC's software registery is updated with new instructions needed to operate that item.  However, when the item is removed, these instructions usually remain on your PC.  Every time you run your computer it tries to execute these instructions but, because the related program can't be found, it causes a registry error.  Your PC is doing a lot more work than it should be and the result is a significantly slower computer.

One of the best ways to manage this is with a neat little tool from Support.com, a Silicon Valley based company.  It's called ARO 2011 and it scans, identifies, and fixes registry errors--resulting in a computer that's a lot more like it was when you first bought it.  On top of the amazing results it offers, it's so easy to install and use that it was recently awarded a coveted 4.5 star rating (out of 5) by CNET's editorial staff and has been downloaded more than 30 million times.

You can now get a free working version of the software which will quickly scan your entire PC and identify all of the registry errors that may be bogging it down.  The free version also scans for junk and checks your PC's baseline security status.  It will eliminate the first 100 errors for free, and if you have more errors that you want to clean up or want to set the program to run on a regular basis (which is recommended), you can easily upgrade to the full version for just $29.95.  After that, registry errors will no longer be a problem.

To get the free version simply click here.

2. Spyware and viruses

Spyware and viruses are software programs that are loaded on your computer without your knowledge or permission.  They have various purposes, including:


  • Changing the default search engine in your browser.
  • Tracking your Web surfing habits and showing you targeted advertising.
  • Using your email program to send out spam to other email addresses.
  • Stealing your personal information.
Most spyware and viruses get onto our computers through files that we download from the Internet or as attachments to emails.  They tend to take up a lot of computing power and, as a result, will significantly slow down your computer.

The simple rule of thumb to follow is to never download any free software programs from companies you do not know and trust, especially screensavers, emoticons, and the like.  In addition, you should never open any attachment to an email unless you are 100 percent certain you know and trust the sender.  In addition, make sure you have a good anti-virus/spyware removal software running at all times.

Follow the above advice and your PC should stay fast and safe.

Flexible future: Forget the iPhone, here's the smartphone made out of 'paper' that will shape with your pocket

The PaperPhone's flexible display makes it more portable that any current mobile computer
In an industry where unbreakable and smaller are best, the world's first interactive paper computer looks set to dominate for years to come.
The PaperPhone has a flexible electronic display that is set to herald a new generation of computers.
Extremely lightweight and made out of a thin-film, the prototype device can do everything a smartphone currently does.
Scroll down for video.


Inventor Roel Vertegaal, the director of Queen's University Human Media Lab in Kingston, Ontario, said: 'This is the future. Everything is going to look and feel like this within five years.
'This computer looks, feels and operates like a small sheet of interactive paper, meaning that when users are reading they don't feel like they are holding a sheet of glass or metal.
'You interact with it by bending it into a cell phone, flipping the corner to turn pages, or writing on it with a pen.'


Its display consists of a 9.5cm diagonal, thin-film flexible E Ink display.
The flexible form of the display makes it much more portable that any current mobile computer - it will shape with your pocket.
Being able to store and interact with documents on larger versions of these light, flexible computers means offices will no longer require paper or printers.
'The paperless office is here,' said Dr Vertegaal. 'Everything can be stored digitally and you can place these computers on top of each other just like a stack of paper, or throw them around the desk.'
Dr Vertegaal will officially unveil his paper computer on Tuesday at the Association of Computing Machinery's Computer Human Interaction 2011 conference in Vancouver.


More Interesting below...
New device lets you kiss over the Internet
Chat with Facebook friends from wristwatch!
Energy saving bulbs can cause cancer
For Sale: 1 Red Ferrari. Made of Wool
I love you, but you can’t have my password
Live Fish and Turtles Sold as Keychains in China
Can an MP3 hack your car?
ICC World Cup 2011 India and Pakistan Theme for Google Chrome
SIM cards can now be used as an ID
Facebook Agrees to Buy Mobile App Developer Snaptu
5 things you should never reveal on Facebook

Japanese researchers have developed technology to let you "kiss" over the Internet. A machine is affixed with a straw that you can move with your tongue, and someone across the world can own a similar unit across the world and "feel" that kiss.

Kissing Transmission
Yet unnamed, the device looks like a box with a straw sticking out its top. It lets you move the straw with the tongue, and via a PC it can translate that same movement to a similar unit anywhere in the world, as long as it's connected online.
Researchers at the Kajimoto Laboratory at the University of Electro-Communications in Japan say the two users, no matter where they are in the world, can feel each other straw movements, which can replicate a kiss.
Fast Company writes the researchers plan to fine-tune other elements of a liplock, including "sense of taste, the manner of breathing, and the moistness of the tongue."
One of the researchers, Nobuhiru Takahashi, notes in a promotional video how the technology can be used by celebrities to give fans "virtual kisses", an idea that has not been proposed before.


He also adds, "Right now the values are handled by one PC, but if a system is put together to handle the values over a network, then it would be easy for this operation to be conducted remotely."
There aren't any details on when this device would be mass-produced and released.


Your wristwatch is no more just a time reminder; you can now update your Facebook pages through it.

A Canadian company called inPulse has created a watch that connects to your smartphone (or PC) and can be programmed to relay instant notifications and alerts, reports News.com.au.

Marketed as the “perfect hacker accessory,” the inPulse watch is fully programmable and can be customised using the company’s SDK.

Developers can take full control over the device’s 1.3″ OLED display, vibrating motor, button, timers and alerts.

inPulse users can also download one of the many apps that have been built for the device including an iTunes controller, PowerPoint Controller, a create-your-own analog clock app, and the FBCheckin app that lets you check into Facebook Places without getting your phone out of your pocket.

The inPulse watch has been in development since 2009 but first appeared on the market in February 2011.

Energy saving bulbs can cause cancer
Their report advises that the bulbs should not be left on for extended periods, particularly near someone’s head, as they emit poisonous materials when switched on.

Peter Braun, who carried out the tests at the Berlin's Alab Laboratory, said: “For such carcinogenic substances it is important they are kept as far away as possible from the human environment.”
The bulbs are already widely used in the UK following EU direction to phase out traditional incandescent lighting by the end of this year.


But the German scientists claimed that several carcinogenic chemicals and toxins were released when the environmentally-friendly compact fluorescent lamps (CFLs) were switched on, including phenol, naphthalene and styrene.
Andreas Kirchner, of the Federation of German Engineers, said: “Electrical smog develops around these lamps.


“I, therefore, use them only very economically. They should not be used in unventilated areas and definitely not in the proximity of the head.”
British experts insisted that more research was needed and urged consumers not to panic.
Dr Michelle Bloor, senior lecturer in Environmental Science at Portsmouth University, told the Daily Express: “Further independent studies would need to be undertaken to back up the presented German research.”
The Department for the Environment insists the bulbs are safe, despite the fact that they contain small amounts of mercury which would leak out if the glass was broken.
Advice on its website states: “Energy efficient light bulbs are not a danger to the public.
“Although they contain mercury, limited at 5mg per lamp, it cannot escape from a lamp that is intact.
“In any case, the very small amount contained in an energy efficient bulb is unlikely to cause harm even if the lamp should be broken.”
The latest report follows claims by Abraham Haim, a professor of biology at Haifa University in Israel, that the bulbs could result in higher breast cancer rates if used late at night.
He said that the bluer light that CFLs emitted closely mimicked daylight, disrupting the body's production of the hormone melatonin more than older-style filament bulbs, which cast a yellower light.
The Migraine Action Association has warned that they could trigger migraines and skin care specialists have claimed that their intense light could exacerbate a range of existing skin problems.

The classified ad might read: "Sports car seeks permanent home, very good condition, one lady owner."
Oh, and another important point: "Made of wool."
After traveling the world for the past five years, British artist Lauren Porter is seeking a permanent home for her knitted red Ferrari sports car.


The arty auto sculpture is named "12 Miles of Yarn" because, well, it took that much wool to knit.

Porter told AOL News the inspiration for her work was the mix of macho high-tech sports car with delicate ladylike handcraft.


"The sculpture is more or less to scale and took about 10 months to build," said Porter, who shuns more traditional knitting projects such as scarves and socks.

"I involved family and friends knitting squares," she explained. "I made a frame out of metal poles which are welded together in sections. The whole piece is flat packable. Being a sculptor, this was the interesting part for me, designing and building the piece.

"The knitting is made up mostly of squares, around 250. I made paper patterns from the frame and knitted and crocheted the other shapes and details by eye. I have never followed a pattern and would be lost if I had to knit a pair of socks!"

"12 Miles of Yarn" has been exhibited in London, Paris and Amsterdam and at both car shows and fine-art galleries. The time has probably come, however, for this particular Ferrari to go up on the blocks.

"It has traveled around over the last five or so years [and] I am now ready to find it a permanent home," Porter said. "I would ideally like it to be on display and enjoyed by the public but am open to any ideas."

Knitting is a central theme in much of Porter's work. Her wool Ferrari was inspired by an earlier series titled "Home Comfort" that featured a knitted chair, woolen toilet and sink.

"I was originally inspired to knit the chair after working with an elderly lady who sat and knitted all day," Porter said.

"Developing that, the toilet and sink were a take on the decoration of covers in the home and the way in which people cover their spare toilet papers with knitted doilies with dolls in them."

What's next?

After a series of sculptures based on hunting trophies -- inspired by a trip across Canada -- Porter is working on a series of quilted British birds.

I recently read a blog post about sharing personal e-mail accounts with your partners or spouse. The blog said about 33 per cent of women and 30 per cent of men share their online information with their partners.

It also said that among unmarried couples, 10 per cent of the time, this led to a discovery of their partner’s infidelity. The figure was lower for married couples – about three per cent.

The identity theft expert who gave these stats, Robert Siciliano, went on to warn that this figure was among those who had admitted to account sharing and discovering the infidelity of their partners. Those who did not own up (and the number of hearts broken) are unknown. It struck a chord somewhere deep inside me.


This brings me to my own little story. Shortly before I broke up with the girl I intended to marry, I almost shared my email/ Facebook information with her. I stopped short of voluntarily giving her access.

I felt that I trusted her enough to share it. However, I believe in respecting one’s privacy even if you are married. Though, I confess I would not have minded if she had given me access to her passwords.

Soon after, a series of events led to the cessation of all ties and I pushed all memories of her to the darkest corners of my mind.

A few weeks later, among the company of friends, an acquaintance who had had a recent break-up of his own, revealed the reality of his girlfriend leaving him was too much to bear.

“I had her Facebook account hacked” he confessed.

“And?” I prodded.

“It was what I had suspected,” he rasped.

“Another guy?” I dared.

A leaden nod followed by a hiss through clenched teeth confirmed that it was true.

Information is indeed a dangerous thing.

I never had anything to hide from my ex. My past exploits were known to her. And even if she had access to my personal accounts, I doubt she could keep up with four of my regularly used accounts and social media, much less my full arsenal of online access points and aliases. But would she want to? More importantly, for what purpose would she use them other than just information?

Looking back, I do find some comfort in the fact that I never shared my information with her, for fear of what use she would put all that information to now that she has no moral or emotional bond with me. Would she discard it or spread it? Would she blackmail me or indulge in cyber-stalking?

I believe that in such a position, one would do what most people usually do when their ex moves out – change the locks.


According to Siciliano, a Michigan man was charged with a felony after he logged into his (now ex) wife’s gmail account to discover she was having an affair.  The charge is computer misuse and he could serve up to five years in prison. He used her password and their shared laptop to gain access to her account. Apparently, marriage does not mean you give up your privacy electronically.

Do you share your e-mail or Facebook passwords or allow your partner to go through your cell phone? Maybe you should think again.

Live turtles and fish to carry around on your key ring is a cute idea. Not so cute, though, for said turtles and fish.
According to Chinese media, the hottest new fad in China involves selling small live-animal key chains. The little turtles and fishes are sealed up in airtight plastic key rings, and sold as trinkets.

Live Turtles Sold as Keychains in China

So how do you feed an animal in an airtight container? The answer: You don't. Vendors reportedly spew off some hodge podge about the water being nutrient rich, but it's not true. The animals, if they're lucky, get to live for a few days. Unfortunately, the whole shebang is legal.

Live Fish and Turtles Sold as Keychains in China

It's sad but true — animal cruelty laws barely exist in China. It was only just recently that the country banned animal circuses, which was a fairly unusual step. Zoos would often make animals perform unimaginable tricks, while dishing up their flesh as exotic entrees at the zoo restaurant.

Man arrested for Eating Dead Bodies of People Bhakkar

5 things you should never reveal on Facebook

5 things you should never reveal on Facebook

-- TNN

You may love being online, but that doesn't mean you can reveal all. Here are somethings that should be kept under wraps:


Intimate photos or videos

Intimate photos or videos

Something that you post in the heat of the moment may come back to haunt you many years later. Anything that's once posted online can never be deleted completely. So make sure that you don't post something that you may not want you colleagues, boss, siblings or parents to see.


Your phone number

Your phone number

And for that matter even your address. Even if you think that you can trust you e-friend, don't be naive. Similarly don't give out you address for some lucky draw. This very lucky draw may prove 'unlucky' for you.


Don't post any abuses

Don't post any abuses

If you have some complaints against you boss or teachers don't write messages against them over the net. For starters, it can be easily traced back to you. Wouldn't you rather talk about your complaints face-to-face with your boss than miss out on that promotion you were vying for.


Bank details

Bank details

It's one thing to pay your bills online over secure websites, but never ever can you give out your account number or your ATM pincodes. Don't take such risk no matter what the emergency is. If someone asks you for such details be suspicious of them.


Minute by minute details

Minute by minute details

It's one thing to tell people how you feel or crack a joke a two over the net, but don't give out details like 'going out for groceries' or 'heading to the local bar'.

--Harshada Rege

Can an MP3 hack your car?

Posted by Unknown | 8:50 AM


Researchers at the University of California, San Diego led by Stefan Savage, and Tadayoshi Kohno of the University of Washington, who have been looking at the vulnerabilities in electronic vehicle controls have found that cars that are built to be friendly with Bluetooth wireless technology have the potential to be hacked using that bond.


The Bluetooth link, which is designed to let your car and your phone work well together has the potential to be exploited in ways that would allow a less than scrupulous individual to upload malicious code to your car using an audio file. So, a song could literally give your car a virus. If you want to go one creepier, the researchers also found ways to pair the cars to a Bluetooth-enabled devices in order to execute that malicious code. So someone could be controlling your car, without you ever knowing it. The code can even be snuck in on an MP3. Burned onto a CD player, and put into your car. When the song is played becomes a Trojan Horse and can then alter the car’s firmware, giving it access to the car’s key systems.
The researchers would not comment on which model of car they had conducted this research on, only that it was a 2009 sedan with fewer computer systems than the average car, but we do know it was not a luxury car.

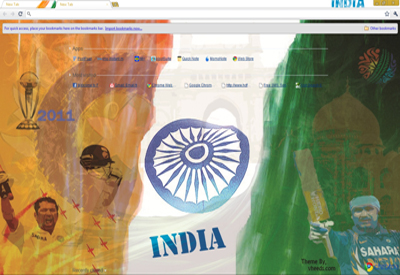
Here is a Google Chrome Theme for Indian And Pakistan Cricket Fans. India and Pakisan Theme for ICC World Cup 2011. Compatible with all resolutions. The theme also comes with India and Pakistan written on the top bar.
Download India Cricket World Cup 2011 Theme


Download Pakistan Cricket World Cup 2011 Theme

Spanish researchers have implemented new software in to regular SIM cards making them secure enough to be used as personal identification

Researchers at Universidad Carlos III de Madrid (UC3M) are developing application to integrate electronic identification data into an mobile phone SIM card so as to use the phone as a means of personal identifications


The prototype was recently presented at the Mobile World Congress in Barcelona, allows secure identification of the user by his eID data stored in the SIM card.


“The SIMs are like small computers that we carry in our mobile devices allowing us to store information and execute applications, with the advantage of providing a high level security,” explained Celeste Campo, the researcher on the project.

How it works

The SIM functions in a relatively simple way: the system obtains the personal information and allows identification and authorisation of the eID stored in the SIM card inserted in the terminal.

Researchers display a regular SIM card with the software implemented and a compatible phone showing a secure personal identification
“These data interact with services offered by the company Secuware and allow us to access the Web services through authentication with the eID,” explained Campo.

The necessary requisites for use of this system are to have an Electronic ID, a PC with a reader for the same purpose, and an Internet connection.

To be installed, the user merely has to indicate his/her telephone number and extract the eID data through a Web site which verifies its validity with the Internet provider.

Following that, a confirmation SMS is sent to the terminal and the information is saved on an SIM card in secure files.

In addition, this information is only accessible for applications with a certificate, which will prevent access by non-authorised third parties.

Future implementation

This system will serve to authenticate in a secure way access to any Web page, especially those of bank services,  and public administrations.

At the moment, the majority of applications which interact with the SIM card are developed in Java ME, code that is not supported by Android and iPhone OS.

For the general utilisation of this system the researchers have to developed an application that can be ported to different mobile devices.

The idea presented is that working in a SIM card would be more autonomous, and as a result, independent of the mobile phone.

Facebook has made yet another plunge in mobile platform to spread its wings. One of the popular social network has finally confirmed the acquisition of mobile platform app developer - Snaptu. Israel based Snaptu which develops apps for feature phones as well as smartphones disclosed the deal on its official blog. As part of the deal, Facebook will pay Snaptu about $60-$70 million and Snaptu would be working as part of Facebook team.

Snaptu develops applications for the feature phones - the phones which aren't smart but possess mobile Internet connectivity and allow installation of Java ME or BREW based apps. Facebook, along with Snaptu, had launched the new Facebook App for popular features phones that consisted of about 2,500 different models. 


Facebook service already has been visible with tighter integration inside the Android OS for INQ handsets and also HTC ChaCha as well as Salsa handsets. That's evidence enough to see how series Facebook is about intoxicating every user with the service. 

With acquisition of Snaptu, we'll get to see the social network's deeper integration in feature phones as well. It won't be surprising to see Facebook centric features phones being launched by year end. In fact, the feature phones segment has large volume of users who don't wish to or can't spend a lot on a smartphone. It's not the first time Facebook has addressed the feature phone segment as earlier the company introduce the 0.facebook.com which was basically image-less version of the service. Let's hope this deal brings us better mobile web experience of the service.